Alleged iOS Security Flaw Enables Malicious Apps to Secretly Log User Touch Inputs - MacRumors
Skip to Content

Alleged iOS Security Flaw Enables Malicious Apps to Secretly Log User Touch Inputs

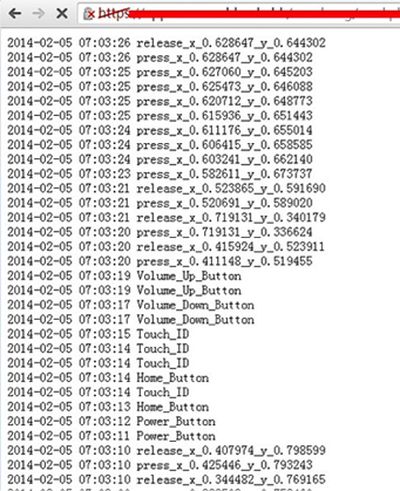
Researchers from security firm FireEye have revealed a new bug in iOS that enables a malicious app to monitor and log a user's touch inputs and button uses while running in the background, reports Ars Technica. The exploit reportedly targets a flaw in iOS' multitasking capabilities to capture user inputs, and allows for them to be sent to a remote server.
fireeye_logging_ios_flaw2
To demonstrate the flaw, the researchers created a proof-of-concept monitoring app and developed approaches to "bypass" Apple's App Store Review process effectively. Once the app was installed on an iOS device, actions including keyboard inputs, use of the volume, home, and power buttons, screen touches with exact coordinates, and Touch ID events were all captured. The researchers also noted that disabling iOS 7's "Background App Refresh" setting would not disable a malicious app from logging data, as the only present solution to the problem is to manually remove apps from the task switcher.

FireEye also spoke about the flaw being identified in current versions of iOS:

Note that the demo exploits the latest 7.0.4 version of iOS system on a non-jailbroken iPhone 5s device successfully. We have verified that the same vulnerability also exists in iOS versions 7.0.5, 7.0.6 and 6.1.x. Based on the findings, potential attackers can either use phishing to mislead the victim to install a malicious/vulnerable app or exploit another remote vulnerability of some app, and then conduct background monitoring.

The group added that it is actively working with Apple on the issue, although the company has yet to comment publicly. The news comes less than a week after Apple issued iOS 7.0.6 in response to a SSL vulnerability that allowed a hacker to capture or modify data from Safari in supposedly secure sessions.

The SSL security bug was also found to be present in OS X, as new research over the weekend revealed that additional apps such as FaceTime and iMessage could be compromised. Apple confirmed to Reuters that it will issue an OS X software update "very soon" to patch the bug.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out in Every Time Zone

Sunday September 13, 2026 3:00 am PDT by
Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event that it will be releasing iOS 27 sometime tomorrow – Monday, September 14. iOS 27 won't be the only release on...
deep black iphone 18 pro

Apple Says iPhone 18 Pro Max Sold in U.S. Differs in One Way

Saturday September 12, 2026 3:27 pm PDT by
As noted by Nicolas Lellouche, who writes for the French tech website Numerama, Apple has updated its tech specs pages for the iPhone 18 Pro and iPhone 18 Pro Max to clarify which models are equipped with its new C2 cellular modem and where. Apple now says the iPhone 18 Pro has a C2 modem worldwide, while the iPhone 18 Pro Max uses the chip in every country except for the U.S. According...
iphone duo

IMAX Reacts to iPhone Duo's 1:1.4 Aspect Ratio Displays

Friday September 11, 2026 4:42 am PDT by
Production theater company IMAX has responded in a mixed way to Apple's embrace of a 1:1.4 aspect ratio on the iPhone Duo's inner and outer displays. The boxier ratio happens to be very close to the classic "full-frame" IMAX 1.43:1 aspect ratio, which comes from the geometry of the company's original 15-perforation/70mm film system. In response to an X post from someone wondering if we'll see...

Top Rated Comments

Asclepio Avatar
164 months ago
welcome to the new microsoft.
Score: 34 Votes (Like | Disagree)
164 months ago
How is this even remotely considered a security issue?

Yes, every touch is logged, but none of the logs carry any semantic information about the touches.

What those guys have just demonstrated is of no use to an actual hacker. It would be like tapping a phone line and then only be able to know how many calls are placed each day.

If you know the exact coordinates you can simply overlay the iOS Keyboard and extract everything the user typed in, including passwords, logins or other personal information. :rolleyes: But yeah, no security issue here. LOL.
Score: 24 Votes (Like | Disagree)
164 months ago
The researchers also noted that disabling iOS 7's "Background App Refresh" setting would not disable a malicious app from logging data, as the only present solution to the problem is to manually remove apps from the task switcher.


those people closing all their apps don't look so silly after all :p:D:p
Score: 19 Votes (Like | Disagree)
164 months ago
How is this even remotely considered a security issue?

Yes, every touch is logged, but none of the logs carry any semantic information about the touches.

What those guys have just demonstrated is of no use to an actual hacker. It would be like tapping a phone line and then only be able to know how many calls are placed each day.
You sure?
The fact that x and y co-ordinates of each touch or release event is captured, could be used as a key-logger once the boundries of each key on the soft keyboard have been worked out.
Score: 18 Votes (Like | Disagree)
164 months ago
S: The group added that they are actively working with Apple to fix the issue, as the company has yet to respond.

Business as usual then......
Score: 15 Votes (Like | Disagree)
164 months ago
Wow.. Apple.. Much secure :rolleyes:
Score: 12 Votes (Like | Disagree)













