Apple will be among several U.S. tech giants to attend a meeting at the White House today to discuss cybersecurity and possible security threats posed by open-source software, Reutersreports.
The meeting will be held by U.S. National Security Advisor Jake Sullivan and will focus on "concerns around the security of open-source software and how it can be improved." The meeting was prompted by concerns around a security vulnerability found in open-source software Log4j.
The vulnerability, which posed a threat to organizations that use Log4j around the world, allowed hackers to control a system and remotely execute malicious code.
According to Sullivan, open-source software such as Log4j presents a "key national security concern" as it is often used and maintained by volunteers. Google, IBM, Meta, Microsoft, and Oracle are also expected to attend the meeting.
Note: Due to the political or social nature of the discussion regarding this topic, the discussion thread is located in our Political News forum. All forum members and site visitors are welcome to read and follow the thread, but posting is limited to forum members with at least 100 posts.
Apple has blocked compromised security certificates on its devices that could help attackers impersonate websites, BleepingComputer reports.
The certificates were issued by certificate authority eMudhra. According to Mozilla's investigation, their private keys were all numbers below 256, making them almost instantly recoverable. Attackers could use the affected website certificate keys to...
Tuesday November 17, 2026 4:41 am PST by Tim Hardwick
Hackers used some of the world's most popular websites to distribute malware designed to steal cryptocurrency and exploit vulnerabilities in iPhones and iPads this week, according to a new security investigation.
Reuters reports that websites associated with 178 organizations were affected by the attack on Monday, November 16, including the likes of Zoom, BBC, CNN, HSBC, Salesforce, and...
Sunday November 15, 2026 8:42 am PST by Joe Rossignol
Bloomberg's Mark Gurman today said Apple has four goals for future iPhone Duo models: Face ID, an Action button, a telephoto camera, and a thinner-and-lighter design. Gurman said Apple has already developed iPhone Duo 2 prototypes with Face ID on the outer display, but it is "running out of time" to finalize the feature for that model, so it might not arrive until the iPhone Duo...
I'm waiting for all the rabbid open-source fans to tell us open-source is much safer than closed-source.
It's not that simple. open-source CAN be safer, it can also be less safe. In open-source, the exact code is out there for anyone to look at. This means anyone could see any flaws and fix them. It also means that anyone could see any flaws and exploit them.
In closed-source, you can't see the code. It's a much different process to exploit the code. Much harder. There are also less people who have access to the code to fix any flaws. So, flaws will stick around longer.
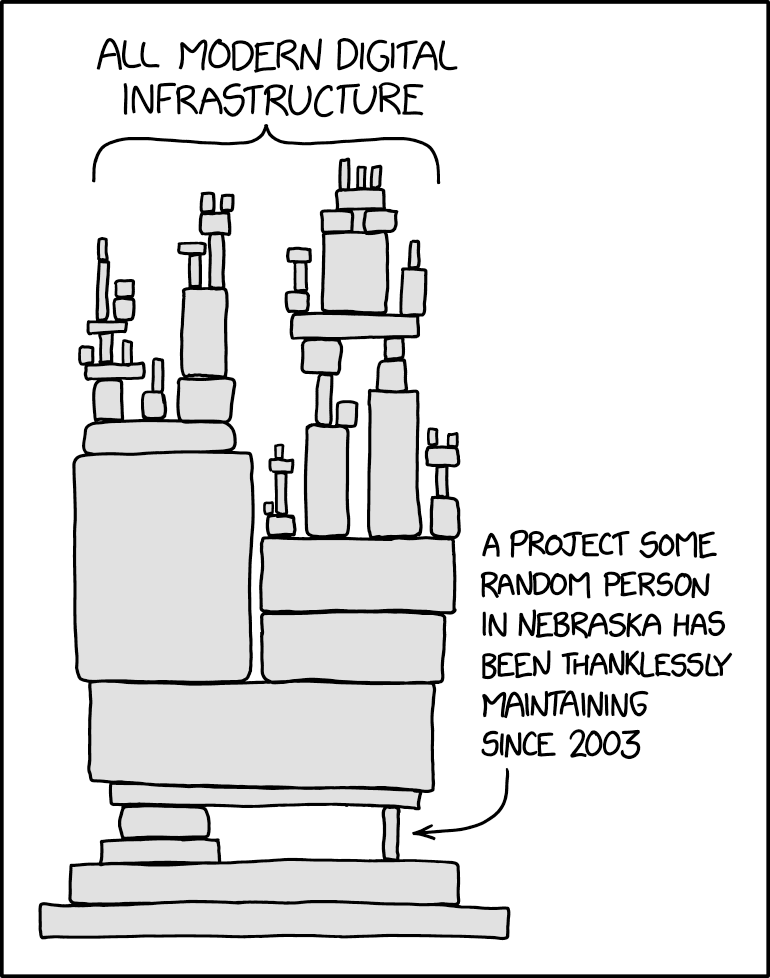
The issue is more that there are a certain amount of core libs that everyone has in their builds. I think now its the Wild West because its no one person/ orgs job to check any of these libs or certify them. … We are leaving for too many core components to be looked after by people for free with no incentive to make sure everything is ok.
The entire Linux community is open source, and yet this is a much more secure platform than Windows has been. And Mac OS and their browsers have heavily benefited from the give and take between Unix and Linux (macOS building on a Unix rather than Linux kernel )
I am almost certain that there have been more security faults in proprietary systems than well maintained open source projects, because the drive behind open source is a more idealistic than the industries “quick to market / milk them all”
With that being said, especially when it comes to web development and the package repositories I see there, I am more doubtful and careful with using and relying on them. I feel it often moves too fast and the community has a different background than e.g. hardcore Linux developers.
I'm waiting for all the rabbit open-source fans to tell us open-source is much safer than closed-source.
It's not that simple. open-source CAN be safer, it can also be less safe. In open-source, the exact code is out there for anyone to look. This means anyone could see any flaws and fix them. It also means that anyone could see any flaws and exploit them.
In closed-source, you can't see the code. It's a much different process to exploit the code. Much harder. There are also less people who have access to the code to fix any flaws. So, flaws will stick around longer.
It's not simple.
Not a rabid open sores fan at all (except back in my teenage years when I went through a rebellious Linux phase ugh), but obscurity does not imply security.