iOS 16 and macOS Ventura Combat Email Spoofing With Support for Verified Brand Logos in Mail App - MacRumors
Skip to Content

iOS 16 and macOS Ventura Combat Email Spoofing With Support for Verified Brand Logos in Mail App

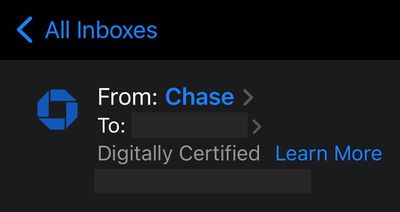
iOS 16 and macOS Ventura add support for the Brand Indicators for Message Identification (BIMI) standard in the Mail app, helping users to easily verify authenticated emails sent by brands by displaying the brand's logo alongside the email's header.
iOS 16 Digitally Certified Mail
In the Mail app, emails sent by brands with a BIMI record are marked with a "Digitally Certified" label, which is visible after tapping to expand the email's header. Next to the label, a "Learn More" link leads to the following message: "This email was verified as coming from the owner of the logo shown and the domain [example.com.]"

For a brand's logo to be displayed, the sender's domain must pass DMARC authentication checks, according to the BIMI Group website. If the email passes authentication, the Mail app queries the DNS for a corresponding BIMI record.

Based on a tweet shared by software engineer Charlie Fish, it appears that Chase Bank is an example of a brand that has implemented BIMI, with the Chase logo appearing next to an email sent by the bank in the Mail app on iOS 16. BIMI is also supported by Gmail, Yahoo Mail, and Fastmail, according to BIMI Group.


This is just one of several new features added to the Mail app on iOS 16 and macOS Ventura, with others including the ability to unsend an email up to 10 seconds after sending it, scheduled emails, notifications if you forget to include an attachment on an email, support for rich links in emails, improved search functionality, and more.


Related Forum: iOS 16

Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
deep black iphone 18 pro

Apple Says iPhone 18 Pro Max Sold in U.S. Differs in One Way

Saturday September 12, 2026 3:27 pm PDT by
As noted by Nicolas Lellouche, who writes for the French tech website Numerama, Apple has updated its tech specs pages for the iPhone 18 Pro and iPhone 18 Pro Max to clarify which models are equipped with its new C2 cellular modem and where. Apple now says the iPhone 18 Pro has a C2 modem worldwide, while the iPhone 18 Pro Max uses the chip in every country except for the U.S. According...

Top Rated Comments

mikethemartian Avatar
55 months ago

While I always welcome features that increase security or privacy, I don't think this will make much of a difference because inattentive or ignorant users are easily fooled by logo graphics attached by scammers to messages. Plus from a behavioral perspective, scammers rely on fear and greed emotions. The human fight-or-flight reflex means that red flags such as obviously bogus URLs, awful grammar, bizarre word choice, or a government agency asking for gift cards are all too often ignored or discounted.
Reminds me of the scene in Catch Me If You Can when Abagnale takes the Pan-Am logos off of model planes and placed them on forged checks.
Score: 8 Votes (Like | Disagree)
55 months ago
Waiting for someone to say this isn’t fair for the spoofers
Score: 4 Votes (Like | Disagree)
surfzen21 Avatar
55 months ago
Even if its not perfect, its definitely a step in the right direction. Knowing is on Apple's radar is a good thing.

I get a lot of these fake emails and had to do a double check on at least a few. Domain spoofers make it even more difficult.
Score: 4 Votes (Like | Disagree)
55 months ago
Excellent move!
Score: 4 Votes (Like | Disagree)
55 months ago
Not a fan of BIMI because it's once again not a solution, but just another overly complex workaround to fixing a broken system.

If all mail-servers required and enfored an organization validated server certificate for inbound connections from other servers the amount of spoofed mails and junk would be reduced by 99+%. Unfortunately, no mail provider can do that alone...

If that was about to be required by law, there would be an instant adoption and the problem essentially solved.
Score: 3 Votes (Like | Disagree)
55 months ago

Apple (or the IETF) needs to replace IMAP. It was written for another age, and it's way long in the tooth.

Basically, security needs to be baked in instead of security as an afterthought. Verified senders needs to be a part of the infrastructure. It's ok to have unverified senders, but they should be marked as-such.

These days, certs are free and processing power is cheap, so issuing everyone a cert and using them for validation shouldn't be as much of a burden as it was back in the day.
No we don't want Apple (or any other big company) to replace IMAP or SMTP or HTTP. Those are the last three major open protocols left that are widely supported, even by the monopolies in email (Microsoft and Google). We should be encouraging their use to keep the Internet open, rather then siloed. Do you want what happened to chat to happen to email? In the past there were open chat standards like XMPP, well just a few days ago Google shutdown Google Talk which supported XMPP, the last widely used chat service to support XMPP. Now you have to decide to use Facebook Chat, Google Chat, Skype, WhatsApps, LINE, etc etc.. all which are siloed and don't communicate with each other or can be run on-premise in your own datacenter. You know how annoying it is for me as a Android phone user when someone uses iMessage to send me something that is not supported in my normal SMS app. I wish Apple would support RCS.

You need to understand email is comparable to phone service (calls and SMS) in the sense it is a widely supported standard, due to it being long in the tooth. These standards are open where anyone can contact you. To deal with spam email or calls, the easy thing to do is only accept them from people on your whitelist you trust. This is how most chat networks work, only people that know you (such as have your phone number in their contacts) can see to add you, which is why you notice less spam.

SMTP already supports sender verification as already described in the forum using SPF and DKIM. The mail server just needs to enforce using it. I don't think they should be blocking email completely just because the SPF or DKIM fails (since many people misconfigure it), but it should cause the mail system to score the email so high it ends up in the spam folder. When it comes to phone calls, they are trying to implement STIR/SHAKEN to combat the same thing with phone calls when it comes to verification to combat spoofing.

Even with email verification it won't completely fix the spam issue since a lot of spam is verified. A lot of email is being sent from hacked email accounts, which will look like they are verified. This means that the root of the issue with this is login authentication. Things are already occurring to improve login authentication, but using a unique hard to guess password for your email account is a major first step. A major second step being MFA. In most instances users pick easy to guess passwords, and even worst reuse that password at other places. Once one of these other places gets hacked, they have your email password. Your email password should be treated like one of you most important passwords, since every service you sign up requires your email for communication, including for security purposes. Simple security practices can go a long way to resolving a lot of issues. If your system gets hacked by way of a virus, then you are completely compromised and nothing will really protect you at that point other then a virus program that can detect and block malicious activity occurring on your system due to the virus infection.

So no we don't want to replace those, we just want to improve them as what have been occurring over the years, such as with HTTP/1.1 moving to HTTP/2, and now HTTP/3, all of which still work in a web browser. Having alternatives is not a problem, but replacing what is already open and supported will just make things more siloed since most of the companies (Google, Microsoft, and Apple) making the decisions do it for their own interests.
Score: 2 Votes (Like | Disagree)