Apple Releases Safari 15.1 for macOS Big Sur and macOS Catalina
Apple today released Safari 15.1 for macOS Big Sur and macOS Catalina, giving Mac users who do not have macOS Monterey installed access to the latest Safari features.
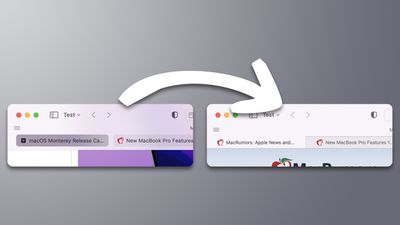
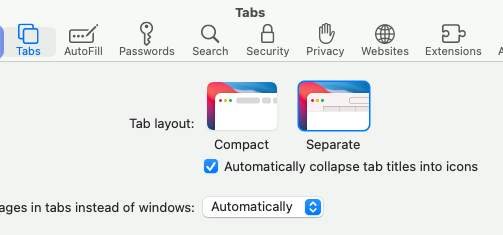
Safari 15.1 reintroduces the previous tab design that was available prior to Safari 15. With Monterey and Safari 15, Apple introduced a new "Compact" look that changed the design of the tabs and unified them with the URL bar, but many people were not fond of that design.
In Safari 15.1, Apple undid those design changes and returned Safari to its pre-Monterey look, doing away with the updated design and the feature that blended the top bar in Safari with the background color of websites. Those who liked the new design can still enable it in Safari preferences, but the old design is the default.
Safari can be downloaded on machines running macOS Big Sur and macOS Catalina by going to System Preferences > Updates. If you have macOS Monterey 12.0.1 installed, you already have Safari 15.1.
Popular Stories
Apple has launched a new "Switch to Safari" marketing campaign that encourages Chrome users to switch to Safari as their web browser of choice on the Mac.
"Safari is a more powerful and private browser than Chrome," says Apple.
Apple has a new "Switch to Safari" page on its website that outlines more than 10 reasons that Chrome users should switch to Safari, including faster performance...
Apple is considering changes to Safari on the iPhone Duo that would give websites access to more of the outer display, although the company has yet to settle on an approach.
The challenge is allowing pages to occupy the area beneath Safari's side-mounted controls without making parts of a website inaccessible. In an Friday, October 23 WebKit post, Apple's Jen Simmons explained that an...
Earlier this month, a security researcher discovered that private cryptographic keys associated with eight of Indian company eMudhra's intermediate certificate authority (CA) certificates were weak. The compromised keys could have allowed attackers to impersonate legitimate websites, potentially putting users' sensitive information at risk. However, there is currently no evidence that the keys...