Apple to Address '0.0.0.0' Security Vulnerability in Safari 18
Apple plans to block websites from attempting to send malicious requests to the IP address 0.0.0.0 on macOS Sequoia, according to Forbes. The means the change will be part of Safari 18, which will also be available for macOS Sonoma and macOS Ventura.
This decision comes after researchers from Israeli cybersecurity startup Oligo Security said they discovered a zero-day security vulnerability that allows a malicious actor to access private data on a user's internal private network. The researchers will present their findings this weekend at the DEF CON hacking conference in Las Vegas.
"Exploiting 0.0.0.0-day can let the attacker access the internal private network of the victim, opening a wide range of attack vectors," said Avi Lumelsky, a researcher at Oligo Security.
The researchers responsibly disclosed the vulnerability to Apple, Google, and Mozilla. More details are available on the AppSec Village website.
macOS Sequoia and Safari 18 are currently in beta and will be widely released later this year.
Popular Stories
Apple has launched a new "Switch to Safari" marketing campaign that encourages Chrome users to switch to Safari as their web browser of choice on the Mac.
"Safari is a more powerful and private browser than Chrome," says Apple.
Apple has a new "Switch to Safari" page on its website that outlines more than 10 reasons that Chrome users should switch to Safari, including faster performance...
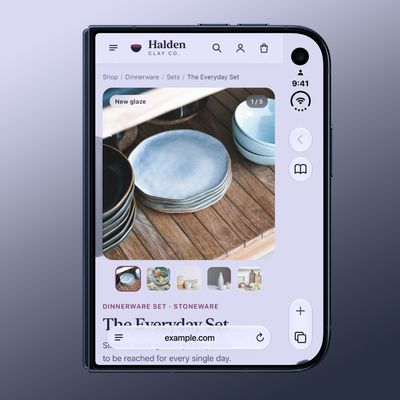
Apple is considering changes to Safari on the iPhone Duo that would give websites access to more of the outer display, although the company has yet to settle on an approach.
The challenge is allowing pages to occupy the area beneath Safari's side-mounted controls without making parts of a website inaccessible. In an Friday, October 23 WebKit post, Apple's Jen Simmons explained that an...
Earlier this month, a security researcher discovered that private cryptographic keys associated with eight of Indian company eMudhra's intermediate certificate authority (CA) certificates were weak. The compromised keys could have allowed attackers to impersonate legitimate websites, potentially putting users' sensitive information at risk. However, there is currently no evidence that the keys...