Apple Launches Open Source Project to Let Password Management Apps Create Strong Passwords - MacRumors
Skip to Content

Apple Launches Open Source Project to Let Password Management Apps Create Strong Passwords

Apple today informed developers that it has launched a new open source project that's designed to let those who develop password management apps create strong passwords compatible with popular websites.
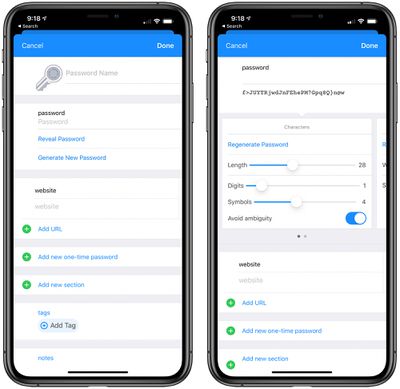
1passwordgenerate
The new Password Manager Resources open source project allows password management apps to integrate website-specific requirements used by the iCloud Keychain password manager to generate strong, unique passwords.

Many password managers generate strong, unique passwords for people, so that they aren't tempted to create their own passwords by hand, which leads to easily guessed and reused passwords. Every time a password manager generates a password that isn't actually compatible with a website, a person not only has a bad experience, but a reason to be tempted to create their own password. Compiling password rule quirks helps fewer people run into issues like these while also documenting that a service's password policy is too restrictive for people using password managers, which may incentivize the services to change.

The project also features a collection of websites known to share a sign-in system, links to website pages where users can change passwords, and more, with full details available on GitHub.

Apple says that having password managers collaborate on resources like password rules and change password URLs allows all password management apps to improve their quality with less work, plus it encourages websites to use standards or emerging standards to improve their compatibility with password managers.


Popular Stories

8 CarPlay Features in iOS 27 Feature

Which iOS 27 CarPlay Features Actually Work in Your Car?

Thursday September 17, 2026 4:17 am PDT by
In iOS 27, available now, CarPlay gets its biggest update in years, but some features depend on what type of car you have rather than your iPhone model. Some of the biggest additions won't do anything in the vast majority of vehicles on the road today. Here's how the new features pan out. Works in Any CarPlay Vehicle Custom widgets: In iOS 27, CarPlay is no longer limited to Apple's handful ...
Apple Watch New Charging Puck

Here's Why a New Apple Watch Charging Puck Was Just Released

Wednesday September 16, 2026 8:53 am PDT by
The new Apple Watch Series 12 and Apple Watch Ultra 4 have hardware changes that allow for faster charging, but you will need to use the new version of the Apple Watch Magnetic Fast Charger included in the box in order to achieve this boost. If you need extra ones for your own charging stands or travel or so forth, Apple released the new version of the charger on its online store last week, with...
ios272anniversary

iOS 27.2 Could Save Your Marriage

Wednesday September 16, 2026 1:32 pm PDT by
The iOS 27.2 beta that Apple released today adds a feature that reminds you it's your anniversary when you call someone, as long as you've added the date in the Contacts app. On the date of your anniversary, when you go to call the person, you'll see a reminder that it's an important day so you don't forget to say something. The anniversary alert uses Call Context, a feature Apple added in...

Top Rated Comments

kop48 Avatar
82 months ago
Any reason why the article shows the password generator from 1Password without references? :)
Score: 21 Votes (Like | Disagree)
82 months ago

there's still going to be (and are) plenty of websites that create their own stupid password rules that no password manager that generates strong passwords will be able to comply. People are still going to have to roll their own- kinda taking away the spark of this project. - But at least it's a step in the right direction.
From the way I read it, that is the goal of this project. Once enough password managers add this feature, it should not matter (from a password generation POV), what the requirements are. The password manager will know BEFORE it generates a password.

Take an example from one of the existing websites in the password-rules.json:

According to the JSON, bhphotovideo.com has a requirement of a password max length of 15 characters. Pretend you go to that website and attempt to create an account. You use the Password Generator in Safari (or any password manager), BEFORE the password generator attempts to create a complex password, it reads the JSON and finds the bhphotovideo.com URL. It then reads the requirements (Max length 15). It immediate creates a password that fits that requirement, regardless of what your defaults are. No action needed on your part to manually change the requirements (which may not be obvious on the webpage.)

The key is (a) the list of password requirements is kept up to date. Since this is published on GitHub, anyone can make a PULL request to update. I wonder what Apple's merge requirements are going to be.

(b) Password managers integrate this in to there workflow.
Score: 14 Votes (Like | Disagree)
82 months ago
The thing I’d really like to see is password generation in safari for 3rd party apps.

It’s a bit of a pain to create new accounts in 1Password with the proper url. You have to go back and forth between the app and 1Password a time or two. It’d be nice if it was more streamlined for 3rd party apps kind of like it is for keychain.
Score: 14 Votes (Like | Disagree)
NightFox Avatar
82 months ago

Any reason why the article shows the password generator from 1Password without references? :)
I'd guess that if they did reference it, people on here would be asking why they'd singled out 1Password to feature over other PWMs
Score: 13 Votes (Like | Disagree)
82 months ago

Sure. Give hackers the open source code to help people generate passwords. What can go wrong? :rolleyes:
Openness enables collaboration. Black boxes maintained by a single company aren't usually the best method for strong security. I want security that shows you exactly what its doing, has been vetted by a community of security experts, and dares the hackers to break it.
Score: 9 Votes (Like | Disagree)
82 months ago
It would be great if websites would have some consistency in their input validation and database schemas. I know one company that allows almost every special character but a comma - and the error message doesn't tell you which special character is the disallowed one. I used 1password and had to go through the generated password and remove each special character 1-by-1 to figure out which one was problematic.
"Hrm, octothorp? Nope. Modulus? Nope. Pipe? Nope. Asterisk? Nope. Greater than symbol? Nope. That just leaves the comma. What?! Seriously?"
It really is an awful experience and I can see why other users would resort to weak and/or reused passwords.
I've see other sites with very specific character length guidelines and other weird combinations. One site, which has since updated to something more secure, even once required 8-15 characters, letters and numbers only. If I were trying to brute force or guess a potentially weak password, wouldn't that make the dictionary size much smaller and thus easier to crack?
Score: 7 Votes (Like | Disagree)














