The U.S. Committee on Energy & Commerce is now seeking answers from Apple over the Group FaceTime flaw that allowed people to eavesdrop on conversations.
Energy and Commerce Chairman Frank Pallone Jr. (D-NJ) and Consumer Protection and Commerce Subcommittee Chairwoman Jan Schakowsky (D-IL) today sent a letter [PDF] to Apple CEO Tim Cook questioning the company about how long it took Apple to address the Group FaceTime flaw, the extent to which the flaw compromised consumer privacy, and whether there are other undisclosed bugs in existence.
"While these are wonderful tools when used right, the serious privacy issue with Group FaceTime demonstrates how these devices can also become the ultimate spying machines. That is why it is critical that companies like Apple are held to the highest standards," Pallone and Schakowsky wrote to Cook. "Your company and others must proactively ensure devices and applications protect consumer privacy, immediately act when a vulnerability is identified, and address any harm caused when you fail to meet your obligations to consumers."
The two representatives ask Apple to be transparent about the investigation into the Group FaceTime vulnerability, and the steps that are being taken to protect consumer privacy going forward. Apple has not been as transparent as "this serious issue requires," according to the letter.
Pallone and Schakowsky ask Apple a number of key questions, including the following:
- When did your company first identify the Group FaceTime vulnerability that enabled individuals to access the camera and microphone of devices before accepting a FaceTime call? Did your company identify the vulnerability before being notified by Mr. Thompson's mother?
- Did any other customer notify Apple of the vulnerability?
- Please provide a timeline of exactly what steps were taken and when they were taken to address the vulnerability after it was initially identified.
- What steps are being taken to identify which FaceTime users' privacy interests were violated using the vulnerability? Does Apple intend to notify and compensate those consumers for the violation?
- When will Apple provide notification to affected consumers?
- Are there other vulnerabilities in Apple devices and applications that currently or potentially could result in unauthorized access to microphones and/or cameras?
Apple CEO Tim Cook will be expected to provide answers to the questions provided in the letter.
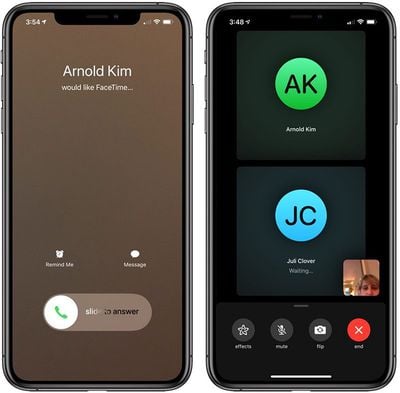
The FaceTime vulnerability came to light last Monday after details spread across social media and news sites quickly picked it up. The bug allowed a person to force a FaceTime call with another person, giving them access to the audio (and sometimes video) from an iPhone, iPad, or Mac without the person ever accepting the FaceTime call.
Apple disabled Group FaceTime on its servers to prevent the bug from being used, and the company is still working on an iOS 12.1.4 update that we are expecting to see this week.
While Apple addressed the bug after it went viral on social media, the company was informed of the issue at least a week before when a teenager discovered it and his mother attempted to contact Apple. Though she sent in multiple reports, they did not go to the right people, and Apple has since apologized and said it is committed to improving the bug reporting process.
Apple is already facing a lawsuit over the Group FaceTime issue and New York officials are also investigating.