macOS High Sierra Vulnerability Allegedly Allows Malicious Third-Party Apps to Access Plaintext Keychain Data - MacRumors
Skip to Content

macOS High Sierra Vulnerability Allegedly Allows Malicious Third-Party Apps to Access Plaintext Keychain Data

macOS High Sierra, released to the public today, could be impacted by a major security flaw that could allow a hacker to steal the usernames and passwords of accounts stored in Keychain.

As it turns out, unsigned apps on macOS High Sierra (and potentially earlier versions of macOS) can allegedly access the Keychain info and display plaintext usernames and passwords without a user's master password.

Security researcher and ex-NSA analyst Patrick Wardle tweeted about the vulnerability early this morning and shared a video of the exploit in action.


For this vulnerability to work, a user needs to download malicious third-party code from an unknown source, something Apple actively discourages with warnings about apps downloaded outside of the Mac App Store or from non-trusted developers. In fact, Apple does not even allow apps from non-trusted developers to be downloaded without explicitly overriding security settings.

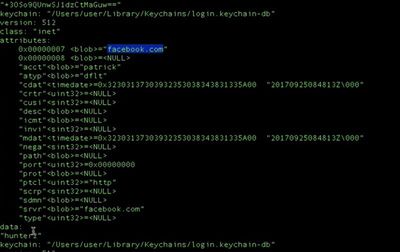
As demonstrated in the video above, Wardle created a proof-of-concept app called "keychainStealer" that was able to access plaintext passwords stored in Keychain for Twitter, Facebook, and Bank of America. Wardle spoke to Forbes about the vulnerability and said it's actually not hard to get malicious code running on a Mac even with Apple's protections in place.
keychainpasswordexploit

"Without root priveleges, if the user is logged in, I can dump and exfiltrate the keychain, including plaintext passwords," Wardle told Forbes. "Normally you are not supposed to be able do that programmatically."

"Most attacks we see today involve social engineering and seem to be successful targeting Mac users," he added. "I'm not going to say the [keychain] exploit is elegant - but it does the job, doesn't require root and is 100% successful."

Wardle has not provided the full exploit code for malicious entities to take advantage of, and he believes Apple will patch the problem in a future update.

As Wardle has not released the full exploit code, it has not been double-checked by MacRumors or another source, so full details on the vulnerability are not known just yet.

Apple has not yet responded to requests for comment about the potential vulnerability.
Related Forum: macOS High Sierra

Popular Stories

iPhone Handoff iOS 27 Feature

T-Mobile to Charge $5 a Month for iOS 27 iPhone Handoff

Thursday September 10, 2026 3:58 pm PDT by
T-Mobile will charge customers $5 per month to use iPhone Handoff, an e-SIM feature that allows the same phone number to be used on two separate iPhones. iPhone Handoff requires carrier support, and at launch, only T-Mobile users in the U.S. and Deutsche Telekom users in Germany will be able to use it. T-Mobile says customers can use their number across two compatible iPhone models and...
iOS 27 Feature Dark

Apple Announces iOS 27 Release Date

Wednesday September 9, 2026 10:46 am PDT by
At its event today unveiling the iPhone 18 Pro, AirPods 5, Apple Watch Series 12, and more, Apple announced that iOS 27 will be released later this month. iOS 27 has already been available as a developer beta since June and as a public beta since July, and Apple today said that the update will be released for all users with a compatible iPhone model on Monday, September 14. iOS 27 is...
iphone duo

IMAX Reacts to iPhone Duo's 1:1.4 Aspect Ratio Displays

Friday September 11, 2026 4:42 am PDT by
Production theater company IMAX has responded in a mixed way to Apple's embrace of a 1:1.4 aspect ratio on the iPhone Duo's inner and outer displays. The boxier ratio happens to be very close to the classic "full-frame" IMAX 1.43:1 aspect ratio, which comes from the geometry of the company's original 15-perforation/70mm film system. In response to an X post from someone wondering if we'll see...

Top Rated Comments

117 months ago
Would have been great if he contacted Apple before the OS was released. Just looking for attention. Jerk
Score: 58 Votes (Like | Disagree)
117 months ago
Would have been great if he contacted Apple before the OS was released. Just looking for attention. Jerk
1. Would have been even greater if Apple had ppl who found these kind of bugs themselves before release.
2. You don't know if he found this yesterday. But sure hate on the guy who might have prevented your bank account password from ending up in the wrong hands.
Score: 52 Votes (Like | Disagree)
bladerunner2000 Avatar
117 months ago
On release day. That's embarrassing.
Score: 38 Votes (Like | Disagree)
carlsson Avatar
117 months ago
OMG, to enable this software you have to enter System Preferences, answer YES on two dialogues, and also enter your password. Then it may STEAL your not encoded things stored in the keychain (by default everything is stored encoded). I think I'm going to Windows now. This is just too much!!!

/irony ended
Score: 34 Votes (Like | Disagree)
s15119 Avatar
117 months ago
sigh. don't download junk, don't jeopardize your computer. Common sense is the best anti-virus.
Score: 21 Votes (Like | Disagree)
bladerunner2000 Avatar
117 months ago
If he did find it yesterday, he should have disclosed it to Apple and given them 90 days to fix it.
He doesn't owe Apple anything. Just like Apple doesn't owe him anything. He did them a favour.
Score: 19 Votes (Like | Disagree)