Third-Party macOS Security Tools Vulnerable to Malware Code-Signing Bypasses for Years - MacRumors
Skip to Content

Third-Party macOS Security Tools Vulnerable to Malware Code-Signing Bypasses for Years

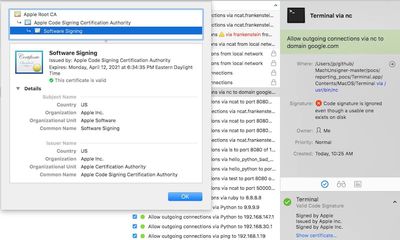
Hackers have had an "easy way" to get certain malware past signature checks in third-party security tools since Apple's OS X Leopard operating system in 2007, according to a detailed new report today by Ars Technica. Researchers discovered that hackers could essentially trick the security tools -- designed to sniff out suspiciously signed software -- into thinking the malware was officially signed by Apple while they in fact hid malicious software.
macos code signing bypass
The researchers said that the signature bypassing method is so "easy" and "trivial" that pretty much any hacker who discovered it could pass off malicious code as an app that appeared to be signed by Apple. These digital signatures are core security functions that let users know the app in question was signed with the private key of a trusted party, like Apple does with its first-party apps.

Joshua Pitts, senior penetration testing engineer for security firm Okta, said he discovered the technique in February and informed Apple and the third-party developers about it soon after. Okta today also published information about the bypass, including a detailed disclosure timeline that began on February 22 with a report submitted to Apple and continues to today's public disclosure.

Ars Technica broke down how the method was used and which third-party tools are affected:

The technique worked using a binary format, alternatively known as a Fat or Universal file, that contained several files that were written for different CPUs used in Macs over the years, such as i386, x86_64, or PPC. Only the first so-called Mach-O file in the bundle had to be signed by Apple. At least eight third-party tools would show other non-signed executable code included in the same bundle as being signed by Apple, too.

Affected third-party tools included VirusTotal, Google Santa, Facebook OSQuery, the Little Snitch Firewall, Yelp, OSXCollector, Carbon Black’s db Response, and several tools from Objective-See. Many companies and individuals rely on some of the tools to help implement whitelisting processes that permit only approved applications to be installed on a computer, while forbidding all others.

Developer Patrick Wardle spoke on the topic, explaining that the bypass was due to ambiguous documentation and comments provided by Apple regarding the use of publicly available programming interfaces that make digital signature checks function: "To be clear, this is not a vulnerability or bug in Apple's code... basically just unclear/confusing documentation that led to people using their API incorrectly." It's also not an issue exclusive to Apple and macOS third-party security tools, as Wardle pointed out: "If a hacker wants to bypass your tool and targets it directly, they will win."

For its part, Apple was said to have stated on March 20 that it did not see the bypass as a security issue that needed to be directly addressed. On March 29, the company updated its documentation to be more clear on the matter, stating that "third-party developers will need to do additional work to verify that all of the identities in a universal binary are the same if they want to present a meaningful result."


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone

Sunday September 13, 2026 3:00 am PDT by
Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event that it will be releasing iOS 27 sometime today – Monday, September 14. iOS 27 won't be the only release today,...
deep black iphone 18 pro

Apple Says iPhone 18 Pro Max Sold in U.S. Differs in One Way

Saturday September 12, 2026 3:27 pm PDT by
As noted by Nicolas Lellouche, who writes for the French tech website Numerama, Apple has updated its tech specs pages for the iPhone 18 Pro and iPhone 18 Pro Max to clarify which models are equipped with its new C2 cellular modem and where. Apple now says the iPhone 18 Pro has a C2 modem worldwide, while the iPhone 18 Pro Max uses the chip in every country except for the U.S. According...
iphone duo

IMAX Reacts to iPhone Duo's 1:1.4 Aspect Ratio Displays

Friday September 11, 2026 4:42 am PDT by
Production theater company IMAX has responded in a mixed way to Apple's embrace of a 1:1.4 aspect ratio on the iPhone Duo's inner and outer displays. The boxier ratio happens to be very close to the classic "full-frame" IMAX 1.43:1 aspect ratio, which comes from the geometry of the company's original 15-perforation/70mm film system. In response to an X post from someone wondering if we'll see...

Top Rated Comments

OldSchoolMacGuy Avatar
108 months ago
These companies are prioritizing speed for security. We can assume they'll now implement proper checks, but it will come at the cost of speed.

I'm sure most won't bother to read this article and blame Apple, but the real blame here is with developers including Little Snitch, xFence, and Facebook's OSquery. They're the ones that failed to properly check these signatures.
Score: 12 Votes (Like | Disagree)
ThunderSkunk Avatar
108 months ago
Wow, but somehow, I'm less concerned about the security threat than I am excited to have discovered the job title "Senior Penetration Testing Engineer". ...someone's up for a performance review & promotion!
Score: 6 Votes (Like | Disagree)
108 months ago
Does Apple give a damn?? Obviously not. It's focused now on important kindergarten stuff like animojis and AR gimmicks.
Score: 5 Votes (Like | Disagree)
108 months ago

I'm sure most won't bother to read this article and blame Apple, but the real blame here is with developers including Little Snitch, xFence, and Facebook's OSquery. They're the ones that failed to properly check these signatures.
It's Apple's fault. When 8 separate developers use the API in the wrong way, there's an issue with the API and instructions.
Score: 4 Votes (Like | Disagree)
slimtastic Avatar
108 months ago
This is very bad. Thank goodness for white-hats who find this stuff out.
Score: 4 Votes (Like | Disagree)
OldSchoolMacGuy Avatar
108 months ago
I'm not sure I'd blame the devs here. The problem is the documentation. Once again reminding us that tech writers are an underappreciated bunch.
The current Apple documentation insists on the need to vet all certificates. But that slows things down, which is why some developers have chosen not to do so.

Is it the states fault if people don't follow speed limit signs?
Score: 2 Votes (Like | Disagree)