Apple Fixes Broken Twitter Links in Safari in Third Beta of OS X 10.11.4
Apple has fixed an issue that prevented shortened "t.co" links on Twitter from loading in Safari on the third beta version of OS X 10.11.4, seeded to developers for testing on Monday, according to developer Dieter Komendera. The bug affected many users in the MacRumors and Apple Support Communities forums.
Since November, Twitter users who click shortened "t.co" links with the secured HTTPS protocol have encountered a bug that prevents content from loading. Oftentimes, when a "t.co" link is clicked, it opens up a blank web page and hangs at a loading screen for several minutes before giving an error message.
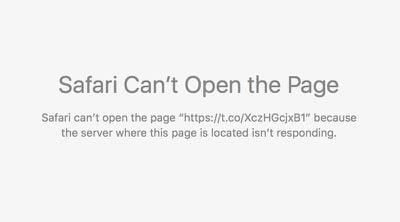
Safari users have used temporary solutions, including reloading the "t.co" link several times, removing "https" from the URL, clearing Safari's cache, or switching to a different browser, but until now there was no official fix yet for the link loading issue. Chrome and Firefox are not affected, nor are links that do not use HTTPS.
Last month, WebKit Developer Experience Manager Timothy Hatcher tweeted that the problem was lower level than WebKit, Safari's underlying rendering engine, and that Apple had a fix identified. OS X 10.11.4 should be released to the public by no later than the end of March, depending on how many beta versions are tested.
Popular Stories
Apple has launched a new "Switch to Safari" marketing campaign that encourages Chrome users to switch to Safari as their web browser of choice on the Mac.
"Safari is a more powerful and private browser than Chrome," says Apple.
Apple has a new "Switch to Safari" page on its website that outlines more than 10 reasons that Chrome users should switch to Safari, including faster performance...
Apple is considering changes to Safari on the iPhone Duo that would give websites access to more of the outer display, although the company has yet to settle on an approach.
The challenge is allowing pages to occupy the area beneath Safari's side-mounted controls without making parts of a website inaccessible. In an Friday, October 23 WebKit post, Apple's Jen Simmons explained that an...
Earlier this month, a security researcher discovered that private cryptographic keys associated with eight of Indian company eMudhra's intermediate certificate authority (CA) certificates were weak. The compromised keys could have allowed attackers to impersonate legitimate websites, potentially putting users' sensitive information at risk. However, there is currently no evidence that the keys...