macOS Keychain Security Flaw Discovered by Researcher, but Details Not Shared With Apple Over Bug Bounty Protest - MacRumors
Skip to Content

macOS Keychain Security Flaw Discovered by Researcher, but Details Not Shared With Apple Over Bug Bounty Protest

German security researcher Linus Henze this week discovered a new zero-day macOS vulnerability dubbed "KeySteal," which, as demoed in the video below, can be used to get to all of the sensitive data stored in the Keychain app.

Henze appears to use a malicious app to extract data from the Mac's Keychain app without the need for administrator access or an administrator password. It can get passwords and other information from Keychain, as well as passwords and details for other macOS users.


Henze has not shared the details of this exploit with Apple and says that he won't release it because Apple has no bug bounty program available for macOS. "So blame them," Henze writes in the video's description. In a statement to Forbes, Henze clarified his position, and said that discovering vulnerabilities takes time.

"Finding vulnerabilities like this one takes time, and I just think that paying researchers is the right thing to do because we're helping Apple to make their product more secure."

Apple has a reward program for iOS that provides money to those who discover bugs, but there is no similar payment system for macOS bugs.

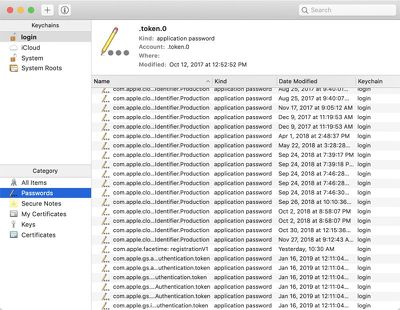
According to German site Heise Online, which spoke to Henze, the exploit allows access to Mac Keychain items but not information stored in iCloud. Keychain is also required to be unlocked, something that happens by default when a user logs in to their account on a Mac.
applekeychain
Keychain can be locked by opening up the Keychain app, but an admin password then needs to be entered whenever an application needs to access Keychain, which can be inconvenient.

Apple's security team has reached out to Henze, according to ZDNet, but he has continued to refuse to provide additional detail unless they provide a bug bounty program for macOS. "Even if it looks like I'm doing this just for money, this is not my motivation at all in this case," said Henze. "My motivation is to get Apple to create a bug bounty program. I think that this is the best for both Apple and Researchers."

This isn't the first Keychain-related vulnerability discovered in macOS. Security researcher Patrick Wardle demoed a similar vulnerability in 2017, which has been patched.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

Scottsoapbox Avatar
99 months ago
How does Apple not have a bug bounty program? Did they start believing their own marketing on Mac OS?
Score: 66 Votes (Like | Disagree)
Goompa Avatar
99 months ago
It doesn’t surprise me. It’s been long time since Apple seemed to care about macOS.

I’m happy for the researcher. Let’s put some pressure on the giant.
Score: 45 Votes (Like | Disagree)
AngerDanger Avatar
99 months ago
Thank god! It was so time-consuming having to double FaceTime call people and wait for them to casually list their passwords as part of natural conversation.
Score: 34 Votes (Like | Disagree)
CE3 Avatar
99 months ago
I understand that finding flaws isn't always an easy thing and can take highly educated/skilled people lots of time to find things like this however no one is forcing this guy to do it.

This sounds a bit like extortion to me.
Extortion implies that not informing developers of bugs is illegal, which it isn’t of course. Apple has likely “reached out” to offer a reward, but he says his motivation is to use this as an opportunity to get a reward program in place for everyone. Good for him. it will probably happen now.

Yes, no one forced him to find this vulnerability, but if you’re a macOS user you should be thankful that he did.
Score: 29 Votes (Like | Disagree)
displaced Avatar
99 months ago
Hmm.

Are Bug Bounty rewards a good idea which provide incentive and reward to bug researchers? Yes. Should Apple have one for macOS? Most likely.

Should a researcher withhold details on a discovered bug as a protest about the lack of a bounty? I don't think so. It seems both unprofessional and dangerous.
Score: 28 Votes (Like | Disagree)
lostngone Avatar
99 months ago
I understand that finding flaws isn't always an easy thing and can take highly educated/skilled people lots of time to find things like this however no one is forcing this guy to do it.

This sounds a bit like extortion to me.
Score: 25 Votes (Like | Disagree)