Unprotected T-Mobile API Let Anyone Get Customer Data With Just a Phone Number - MacRumors
Skip to Content

Unprotected T-Mobile API Let Anyone Get Customer Data With Just a Phone Number

A security vulnerability in T-Mobile's website let anyone gain access to the personal details of any T-Mobile customer using just a phone number, reports ZDNet.

An internal T-Mobile employee tool, promotool.t-mobile.com, had a hidden API that provided T-Mobile customer data when a customer's cell phone number was added to the end of the web address. Data that was available included full name, address, billing account number, and for some customers, tax identification numbers.
tmobile logo
Account data, such as service status and billing status was also included, but it does not appear that credit card numbers, passwords, or other sensitive information was compromised. ZDNet says that there were "references to account PINs used by customers as a security question" which could be used to hijack T-Mobile accounts.

The API was used by T-Mobile staff to look up customer data, but it was accessible to the public and not protected by a password. T-Mobile rectified the issue in early April after it was disclosed by security researcher Ryan Stevenson, who ultimately earned $1,000.

In a statement provided to ZDNet, T-Mobile says that it does not appear customer data was accessed using the API, but research suggests the API had been exposed since at least October 2017.

A T-Mobile spokesperson said: "The bug bounty program exists so that researchers can alert us to vulnerabilities, which is what happened here, and we support this type of responsible and coordinated disclosure." "The bug was patched as soon as possible and we have no evidence that any customer information was accessed," the spokesperson added.

This is not the first unprotected API issue that T-Mobile has faced. Last year, a similar bug also exposed customer data to hackers.

T-Mobile has more than 74 million customers, and had this most recent bug been exploited, a simple script could have provided hackers with access to data on millions of people.


Popular Stories

iPhone Handoff iOS 27 Feature

T-Mobile to Charge $5 a Month for iOS 27 iPhone Handoff

Thursday September 10, 2026 3:58 pm PDT by
T-Mobile will charge customers $5 per month to use iPhone Handoff, an e-SIM feature that allows the same phone number to be used on two separate iPhones. iPhone Handoff requires carrier support, and at launch, only T-Mobile users in the U.S. and Deutsche Telekom users in Germany will be able to use it. T-Mobile says customers can use their number across two compatible iPhone models and...
iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...

Top Rated Comments

109 months ago
Pro tip from someone that works in Information Assurance, and has been involved in cleaning up several companies’ similar messes: anytime you see “we have no evidence that any customer information was accessed”, you can assume that they have zero logging. They ‘have no evidence’ because they have no logs; they aren’t saying it didn’t happen, it’s just a nice way to make it seem like nothing bad happened. Ask for evidence proving nothing bad happened, and you’ll be met with a horrified stare.
Score: 19 Votes (Like | Disagree)
109 months ago
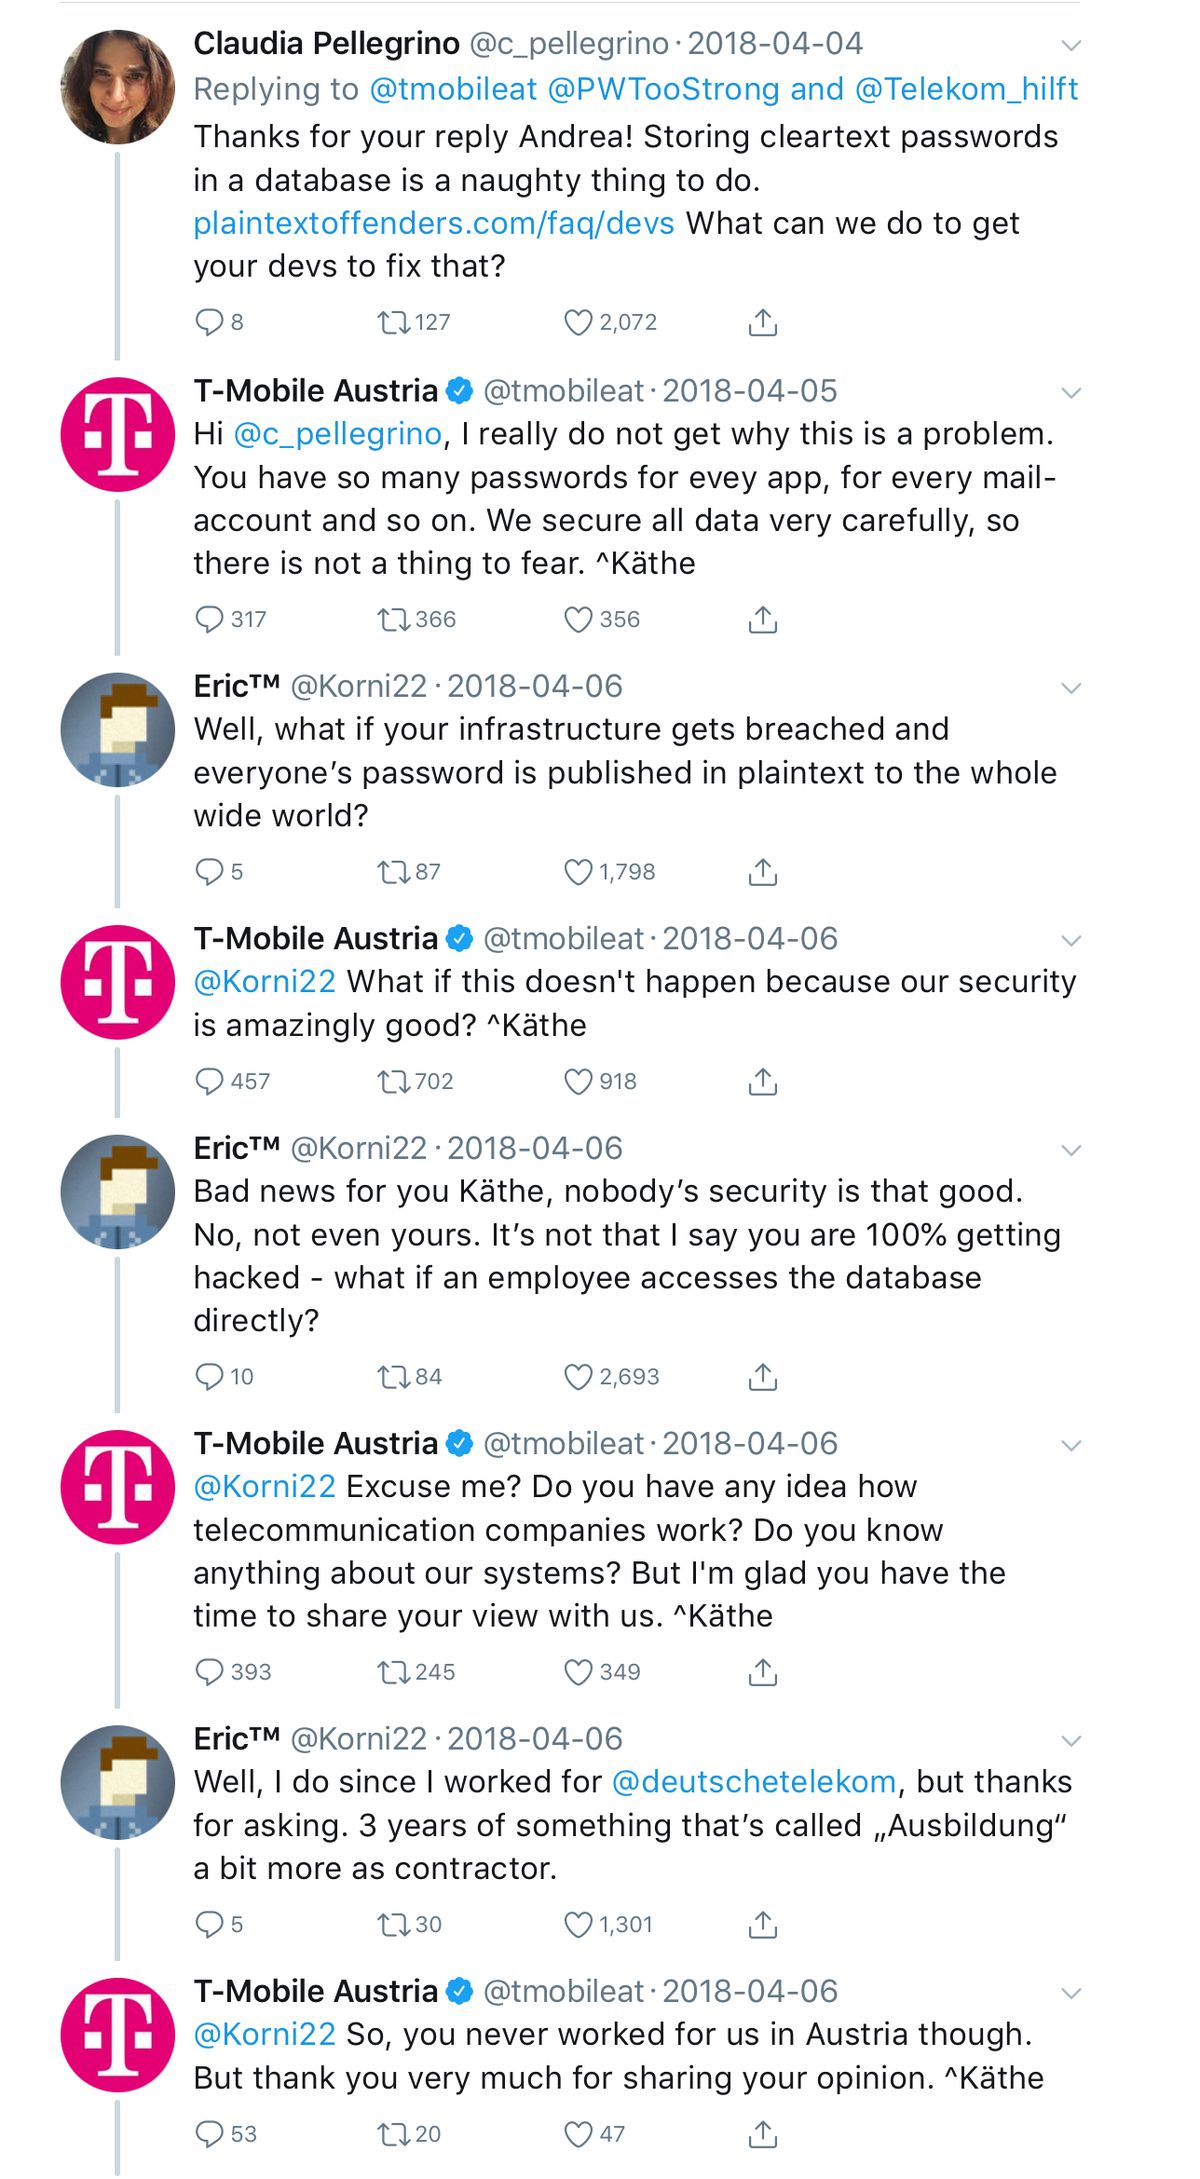
Makes me think back to this conversation with TMobile on Twitter about the passwords being stored in plaintext (though it was TMO Austria).

https://twitter.com/tmobileat/status/981418339653300224

“Our security is amazingly good” LOL


Attachment Image
Score: 16 Votes (Like | Disagree)
Analog Kid Avatar
109 months ago
Until we start punishing these stupid mistakes with penalties that actually hurt, this is just going to happen over and over...
Score: 15 Votes (Like | Disagree)
PlainviewX Avatar
109 months ago
Only $1000 for a catastrophic possible breach discovery? That's like getting paid $45 in a contest that was used as the Mets logo.
Score: 9 Votes (Like | Disagree)
brinary001 Avatar
109 months ago
Damn. Glad I switched to AT&T recently
Score: 2 Votes (Like | Disagree)
Jaspio Avatar
109 months ago
Makes me think back to this conversation with TMobile on Twitter about the passwords being stored in plaintext (though it was TMO Austria).

https://twitter.com/tmobileat/status/981418339653300224

“Our security is amazingly good” LOL

LOL never let a glorified marketing drone talk technology. They can only embarrass their company and expose it to malpractice suits.
Score: 2 Votes (Like | Disagree)