New OS X 10.10.5 Privilege Escalation Vulnerability Discovered - MacRumors
Skip to Content

New OS X 10.10.5 Privilege Escalation Vulnerability Discovered

by

Just days after Apple patched the DYLD_PRINT_TO_FILE security hole with the release of OS X 10.10.5, a developer has found a similar unpatched exploit that could allow attackers to gain root-level access to a Mac.

Luca Todesco shared information (via AppleInsider) on the "tpwn" exploit on GitHub over the weekend. It affects all versions of OS X Yosemite, including OS X 10.10.5, but does not affect OS X El Capitan.
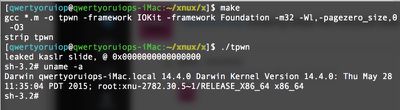
tpwnvulnerability
Todesco did not give Apple a heads up on the vulnerability before sharing it publicly, so it is not clear when Apple will release a patch for machines running OS X Yosemite. As noted by AppleInsider, it is standard procedure (and a courtesy) for security researchers and developers to provide Apple with details on vulnerabilities before publicizing them to prevent hackers from using security holes for nefarious purposes.

According to Todesco, who has also shared what he says is a third-party fix, releasing details on the exploit is no different than releasing an iOS jailbreak, but as Engadget explains, Todesco's actions have the potential to be somewhat more harmful than a jailbreak.

Those are technically true, but they downplay the practical dangers of publishing this info. Many people aren't knowledgeable enough to try third-party safeguards or deal with the possible side effects, and jailbreaks are at least intended for semi-innocuous purposes. A 'surprise' exploit for the Mac only really serves to give attackers time that they wouldn't otherwise have.

It took Apple less than a month to release OS X 10.10.5 to fix the DYLD_PRINT_TO_ACCESS vulnerability after it was first publicized, but during the time between its discovery and the launch of the fix, an exploit using the vulnerability was discovered in the wild.

Ahead of a fix for this latest vulnerability, OS X Yosemite users can protect themselves by downloading apps solely from the Mac App Store and from trusted developers.


Top Rated Comments

146 months ago
I read somewhere that he only gave Apple a few hour's notice before releasing it. He's a scumbag. And I have to say that the writer of this article is sort of a scumbag if that screenshot is the code for the vulnerability (If this is true, sorry Juli).
The screenshot is just a proof that compiling some code and running it works. However, not giving a company any chance to release a fix is something only a complete jerk would do.


Score: 10 Votes (Like | Disagree)
146 months ago
The screenshot is just a proof that compiling some code and running it works. However, not giving a company any chance to release a fix is something only a complete jerk would do.
Perhaps he had good reasons for doing this. For example, he might have evidence that the bug is already being exploited. If true, people can immdiately use the third-party fix he pointed to rather than waiting around for Apple to fix it. After all, they sometimes takes their sweet time ('http://krebsonsecurity.com/2011/11/apple-took-3-years-to-fix-finfisher-trojan-hole/') ...

Also, I think his comparison to jailbreaks is apt. Essentially whenever a jailbreak is released, the jailbreakers publish privilege escalation bugs and a nice demo on how to exploit them.

Finally, one should keep in mind that he could just as well have sold the exploit on the black market for a fat check instead of just publishing it and then getting called "complete jerk" as a reward ...
Score: 7 Votes (Like | Disagree)
bradl Avatar
146 months ago
Front page news, surely?

Seems that it is now a race between Apple and malware writers make use of this information.
Again, this isn't of much use unless the attacker has physical or network access to your Mac. That isn't to say that this isn't any less of a vulnerability than those they've fixed, but this one also isn't something that someone can target a Mac with remotely, and instantly have root access.

tl;dr: a lot of variables have to fall into place at the right time for this to have any major impact to a single machine.

BL.
Score: 6 Votes (Like | Disagree)
bradl Avatar
146 months ago
I read somewhere that he only gave Apple a few hour's notice before releasing it. He's a scumbag. And I have to say that the writer of this article is sort of a scumbag if that screenshot is the code for the vulnerability (If this is true, sorry Juli).
close.. the screenshot is of the code being compiled by a non-root user and executed by the non-root user, showing how the privileges are escalated to become root.

Doesn't take away the fact that the guy was an idiot for releasing this the way he did.

Funnily enough, @i0n1c has a patch that can be applied to this.

BL.
Score: 6 Votes (Like | Disagree)
146 months ago
That may be true, but developers have a set of ethics (s)he should abide by.
If you want to assign developers ethics, then I guess you should start by mentioning the OS developers' ethics (meaning, Apple's). Apple:

* doesn't offer bug bounties
* sometimes doesn't even react to the bug reports
* when there's a reaction it uses to take months or more (and still some people praise them!?)
* doesn't always acknowledge the bug reporter
* doesn't EVEN make it easy to report and track bugs

So, again, what developer ethics are you talking about?
Score: 5 Votes (Like | Disagree)
bradl Avatar
146 months ago
For the average user? Sure. But I know at least one university that is very nervous about their multiple computer labs full of iMacs. It's a pretty big deal.
That's my point. If deployed in a lab, university, or enterprise environment, this could be severe. All it takes is compiling it one place for one type of architecture for it to be distributed to any other Mac.

However, in a lab or Enterprise environment, where it is mainly iMacs, they aren't going to be as portable. So Find My Mac wouldn't really need to be enabled on those, so the Guest Account wouldn't need to be enabled, allowing unfetted, password-free access to the iMac. If tied to some sort of Directory protocol (Active Directory, LDAP, etc.), such work could be traced to the person that released it. So while it may be a big deal, that university could easily bait this as a trap for the malevolent user.

That security researcher doesn't owe you or the richest company in the world anything. He's free to do whatever he wants.
That may be true, but developers have a set of ethics (s)he should abide by. He is showing a complete lack of ethics in the way that he released this. On every security list I have been on (including Secunia and Bugtraq) the discoverer of the vulnerability always would let the vendor know of the vulnerability and give them time to patch it before announcing the vulnerability. Even the JB teams here (TaIG, Pangu, evad3rs) do that. This guy did not.

If you think that is fair for him to do, perhaps you should reexamine your ethics as well.

BL.
Score: 4 Votes (Like | Disagree)

Popular Stories

apple pro tell logo

Apple Launching Five New Products This Friday

Monday November 2, 2026 1:22 am PST by
Apple is releasing five new products this Friday, November 6, following pre-orders that opened last week, including its first touchscreen MacBook Pro models. The following new products will be available from Friday: iPad mini with OLED display and A20 Pro chip iMac with M6 chip 14-inch MacBook Pro with M6 chip 14-inch MacBook Pro with OLED touchscreen 16-inch MacBook Pro with OLED...
Apple Logo Gradient 16x9 1

Apple Isn't Done With 2026: Here's What's Still Coming

Monday November 2, 2026 7:27 am PST by
Apple's busiest season isn't over yet. Far from it. With two hardware launch dates still to come in November, plus software updates and new smart home accessories running into December, there's more on the way from Apple before the end of 2026, so be sure to stick around. Below, we've rounded up what's still coming, along with one date in particular that's worth watching if you're a holiday...
Apple Store Logo

Apple Store in UK Permanently Closing Later This Month

Tuesday November 3, 2026 7:34 am PST by
Apple today announced that its Festival Place store in Basingstoke, England will be permanently closing on Saturday, November 21. Apple Festival Place Apple had already announced that the store would be closing in November, but it had not provided the public with a specific date until now. Apple's store inside the Festival Place shopping center opened in 2011, so it had a 15-year run....
Latest Stories
Apple Launching Five New Products Tomorrow
49 minutes ago
Apple Releases Safari Technology Preview 256 With Bug Fixes and Performance Improvements
9 hours ago
Apps Can Now Try to Stop You From Canceling Subscriptions
10 hours ago
'Super Mario Odyssey' Can Now Run on Apple TV Thanks to AI
10 hours ago
How 'Resident Evil' Director Zach Cregger Uses His iPhone to Make Movies
12 hours ago
HomePod Mini 2's Amount of RAM Confirmed
12 hours ago
Apple TV's '12 Days of Snoopy' Special Arrives November 13
12 hours ago
Apple is Putting Employees on an AI Budget
13 hours ago
Apple Releases Xcode 27.3 Beta With Three New Features
14 hours ago
Apple Will Check Public iCloud Links for Harmful Content Starting in iOS 27.3
15 hours ago
macOS 27.3 Brings Live Activities to Macs Without Dynamic Island
16 hours ago
Apple TV Reportedly Planning 'Silo' Spinoff
17 hours ago
Is It Worth Buying a Titanium Apple Watch?
17 hours ago
macOS 27.3 Includes an Important Security Fix
17 hours ago
Massive Sale Hits Apple Watch Ultra 3 With Record Low $250 Discounts
19 hours ago
Does HomePod Mini 2 Have Improved Sound? Here's What Reviews Say
19 hours ago
macOS 27.3 Makes Markdown Files Easier to Read
19 hours ago
HomeView Pre-Order Returns to $289.99 on Amazon
20 hours ago
Apple May Phase Out Non-Touch High-End MacBook Pros
20 hours ago
Apple's Insider Trading Policy Now Covers Prediction Markets
21 hours ago
'Stick' Season 2 Premieres Today on Apple TV
21 hours ago
iPhone 18e Rumored to Focus on Chip Upgrade With Few Major Changes
21 hours ago
Google Maps Updated to Fully Support iPhone Duo Displays
21 hours ago
Everything New in the iOS 27.3 Beta
1 day ago
Apple Music's New Selfie Sing Feature Lets You Record Karaoke Videos
1 day ago
iPhone Jailbreak Gets Past Lockdown Mode and Survives an Update
1 day ago
iPadOS 27.3 Expands Siri Mode to Camera App
2 days ago
Veterans Day Apple Watch Activity Challenge Launches November 11
2 days ago
Best Early Black Friday Mac Deals: Save Hundreds on MacBook Air, Mac Mini, and More
2 days ago
Apple Fitness+ Gets Gym Strength Plans in iOS 27.3
2 days ago








































